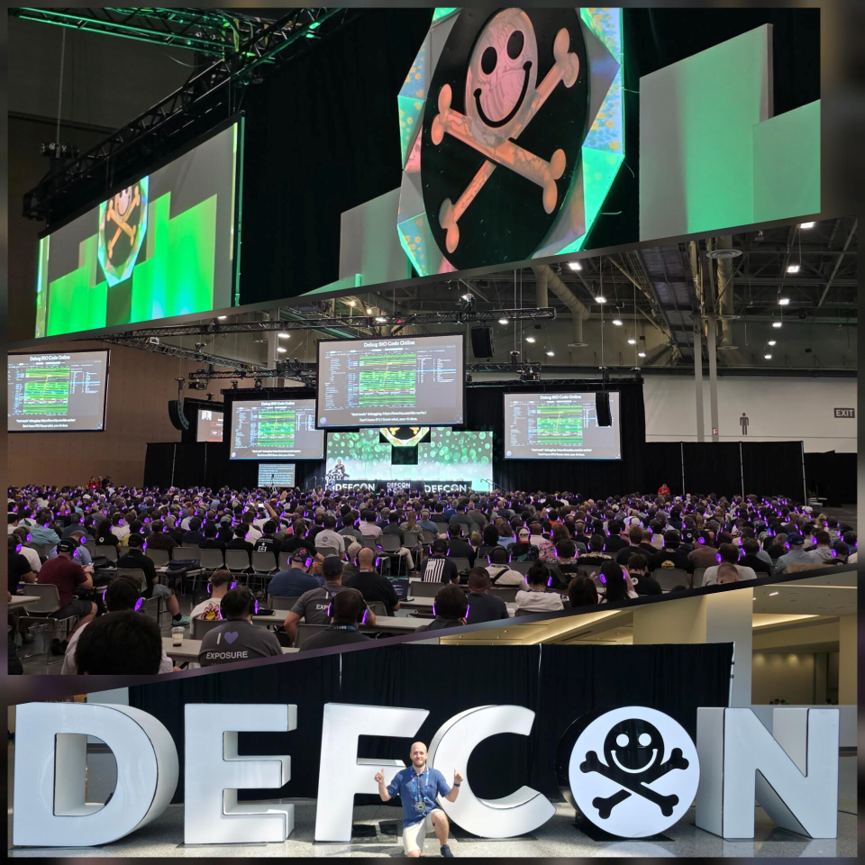
Being part of the cybersecurity community means more than simply following the news or reading security research. It is about getting involved, having conversations, sharing experiences, discussing problems, and learning from peers who face similar operational challenges. Of course, all of this comes with an investment of time, energy, and a full day of travel to reach one of the world’s largest hacking conferences: DEF CON in Las Vegas.
This year, I had the opportunity to attend DEF CON 34 and step away from the day-to-day operational pressures of running a SOC. The value of this experience goes far beyond the conference itself. It is about bringing knowledge, fresh ideas, and external perspectives back to the team and using them to challenge and further shape our roadmap at OBRELA.
Sometimes, stepping away from daily operations allows you to look at familiar challenges from a completely different angle. Problems that appeared to be blockers suddenly reveal alternative solutions, while key areas for improvement become much clearer. Experiencing this shift in an environment like DEF CON makes it even more valuable, as you are constantly exposed to emerging research and practitioners who challenge conventional security thinking.
From attending presentations featuring unreleased or unpublished research to long technical sessions, hands-on workshops, and exploring villages dedicated to Blue Team, Red Team, Malware, AI, and Physical Security, there was always something new to absorb. But the most valuable element was the community itself: exchanging ideas with security professionals, hackers, and researchers from across the globe and seeing how others tackle the exact same operational hurdles.
Key Takeaways for SOC Operations
One of my strongest takeaways was that the fundamentals still matter.
AI is rapidly becoming a cornerstone of cybersecurity, and OBRELA is actively exploring this space, as demonstrated by our recent whitepaper. At DEF CON, the community’s focus on AI was undeniable, with clear use cases spanning detection, investigation, threat hunting, and analyst assistance. However, a recurring theme was that we must not let new technology distract us from core security hygiene**—because** attackers certainly do not. If a simple technique works with minimal effort, an adversary has no reason to deploy anything more complex or sophisticated.
A stark example of this was the focus on social engineering and vishing in the Recon Village. One live demonstration, conducted from a soundproofed booth, showed how easily employees can be manipulated into revealing sensitive credentials and information through a single phone call. It was a potent reminder that even advanced technical controls can be bypassed through human manipulation.
Furthermore, attackers are now leveraging AI**—through** deepfakes, voice cloning, and other AI-assisted tools**—**to make these social engineering tactics significantly more convincing. Ultimately, while we invest in AI to strengthen our defences, adversaries use it to refine their execution and improve their attacks. The tools evolve on both sides, but the fundamentals of security and the human factor remain critical.
Another highlight was the research surrounding active APT groups. Several sessions demonstrated how researchers manipulated and trapped members of known threat groups, exposing their infrastructure, tools, internal structures, and**,** in some cases, their true identities. For a SOC, these insights shift our focus beyond the detection of simple adversary indicators and towards a deeper understanding of real-world adversary behaviour.
The examples above capture only a small sample of the research presented across the conference villages. To keep this update focused, I have highlighted the insights that stood out most for our operations. However, the full schedule of presentations and technical talks is available on the official DEF CON website for anyone keen to explore further.
Bringing the Knowledge Back to OBRELA
The true value of an event like DEF CON is what happens after we return. The techniques, intelligence, and ideas gathered must find their way back into our daily SOC operations**—**influencing our detection logic, playbooks, automation, and overall strategy.
DEF CON 34 was a clear reminder that cybersecurity never stands still. As tools, technology, and threat actors evolve, our SOC must continuously adapt. Being active in the global community allows us to learn not only from what is already documented, but also from what is actively being researched and discovered on the front lines. That is precisely what we bring back to OBRELA: sharper insights, new ideas, and a stronger posture to defend our clients while continuing to develop and strengthen our SOC.